[THE FASTEST SANDBOX IN THE WORLD]
Speed & persistence
Flagship 25ms resumes give your agents absolute autonomy and context persistence at instant speeds.
Boot in milliseconds
Provision a fresh, isolated microVM and connect under one second, so agents can start working immediately.
World-class 25ms resume times
Resume from standby in 25 milliseconds with full memory state restored, at any time.
Fully stateful machines
Sandboxes are persisted forever across sessions with filesystem & memory snapshots, so you never have to restart processes on resume.
Auto-suspended when idle
Sandboxes scale to zero after a few seconds of network inactivity, so you never pay for compute you don't use.
RAM-speed filesystem
The root filesystem runs in memory, keeping reads and writes at RAM speed for almost every operation.
Automated cleanup
Set lifecycle policies to automatically delete or archive sandboxes that will never be reused.
“Other providers take minutes to spin up a sandbox. Blaxel takes milliseconds.”
[GIVE A COMPUTER TO YOUR AGENT]
Agent-native environment
Blaxel Sandboxes are AI-native: a high-performance OS-as-a-service that gives every agent full Linux access to filesystems, libraries, shells, and logs.
Checkpoint everything
Capture files and running processes in one snapshot, then roll back to that exact state whenever you need.
Fork into parallel sandboxes
Branch into new sandboxes so agents can explore, test, and work in parallel without rebuilding their environment.
Tool-call native
A built-in MCP server in every sandbox gives agents instant access through remote tool calls.
Full control over the terminal
Start and manage processes, run arbitrary commands, and stream stdout and stderr live from every sandbox.
Event-driven automation
React in real time to file and directory changes inside the sandbox.
Keep humans in the loop
Use public or private preview URLs to expose sandbox applications safely to end users.
Schedule background agents
Run commands on a recurring cron, at a future date, or after a delay without an external scheduler.
Open-source core
Blaxel's sandbox API is fully open-source.
[STORAGE]
Persist context and AI-generated code for years
Snapshots that outlive sandboxes
Keep named, workspace-level snapshots after their source sandbox is gone, ready to restore or fork later.
Guaranteed retention for years
Block-storage-based Blaxel Volumes retain data for years with a fully redundant solution.
Share context across workloads
Reuse the context persisted in one sandbox across other workloads with Blaxel Agent Drive.
Own your networking layer
Custom domains
Expose services running in a sandbox on your own domains, with managed TLS.
Proxy
Inject secrets with a managed egress proxy, so credentials never live in the sandbox.
Fixed egress identity
Dedicated static IPs so downstream systems can allow-list your agentic traffic.
Dynamic firewall
Restrict egress by domain, HTTP method, and path.
[BUILT FOR SCALE AND SECURITY]
Isolation, compliance & scale
Hardened security and elastic infrastructure for your most demanding AI workloads with total control.
Enterprise compliance
Security-first architecture certified to the standards enterprises require: SOC 2, HIPAA, ISO 27001. Visit the compliance portal.
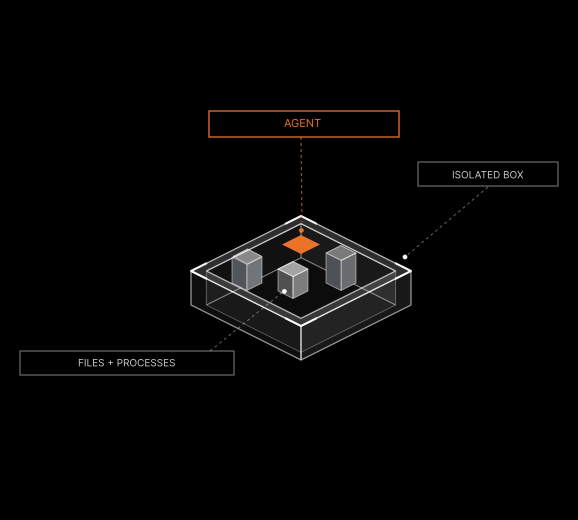
Hardware-level isolation
Every sandbox runs in its own microVM with no shared kernel.
Zero data retention
Each sandbox runs with the root filesystem in memory, so all data is wiped forever when the sandbox is destroyed.
Region support
Choose deployment regions for local data residency, with Europe and US regions available.
Scale to 100,000+
Scale to 100,000+ concurrent sandboxes and up to 512 TB of storage with a tier-based quota system.
[BUILT FOR AI USE CASES]
AI builders run sandboxes to power their products from agentic code execution to data wrangling.
Coding agents and app builders
Materialize a runnable app the moment a user prompts, keep it warm on standby, and resume it in 25ms when they come back.
Data wrangling
Run untrusted, AI-generated transformations against real data with RAM-speed filesystems and hard isolation per job.
AI code review
Review agents analyze repositories in fully isolated, per-tenant environments, kept snapshotted in standby between sessions so there's no need to re-clone.
Computer use and browsing
Give agents a full Linux desktop and browser per session, with outbound control on everything they reach.